4. Common tasks
These are the everyday lifecycle actions (available to Operators and Admins).
Onboard a new employee
- Start an Onboarding workflow.
- Provide the person’s details (name, department, role, licenses/groups).
- Submit — the app creates the account, assigns licenses/groups and, on hybrid tenants, can trigger on‑demand Cloud Sync so the user appears quickly.
Assigning access (step 3). Access is grouped into clear sections:
- Security groups, Microsoft 365 groups (Microsoft 365‑Gruppen, its own section), distribution lists, licenses and teams — tick what the new hire needs.
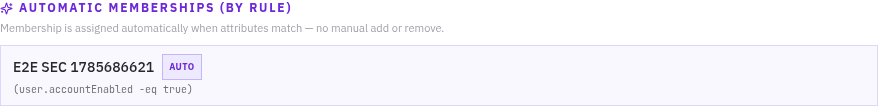
- Automatic memberships (by rule) — dynamic (rule‑based) groups are shown here read‑only with an Auto badge and their rule. You don't select them; the person is added automatically once their attributes match.
- Hide new employee from the address book (Aus dem Adressbuch ausblenden) — optional switch (off by default) to hide the new mailbox from the Global Address List.
Seat guard
If a licensing group you tick has no free seats, the form warns you and blocks the create until seats free up (or you pick another group). See Seat usage.
See Groups, distribution lists & the address book for the group types and the address/alias options.
Offboard / disable an employee
- Start an Offboarding workflow for the user.
- The app disables the account and applies your offboarding steps (revoke access, etc.).
- On hybrid tenants, users mid‑sync are flagged so you know when the change has propagated.
Shared mailbox on leave
When licenses are removed on offboard and Shared‑mailbox‑on‑leave is enabled, the person's mailbox is converted to a shared mailbox (renamed, hidden from the address book, with an auto‑reply) and kept for a retention period instead of being deleted — so colleagues keep access to the mail. Admins can extend the retention or reactivate the person later. See Offboarding & shared mailboxes.
Rehire someone (reentry)
If a former colleague comes back, you don't start from scratch. On the Leaved employees list, users whose account still exists show a green “Reaktivierbar” badge (use the “Nur reaktivierbare” filter to see only them). Open the person and click Neueintritt — or, in Onboarding → clone from user, pick the leaver and choose Reentry.
A short dialog shows exactly what will be restored — groups, distribution lists, Teams, licenses and shared mailboxes — before you confirm. Reentry re‑enables the account, converts a grace‑period shared mailbox back to a normal mailbox, and puts back their old access. A welcome‑back email can automatically go to the person's manager (see Offboarding & shared mailboxes → Reentry).
Managing an employee's access & address book
On the Employee details → Access tab you can add/remove security groups, Microsoft 365 groups, distribution lists, licenses and teams. Two things behave specially:
- Rule‑based groups are read‑only. Any dynamic group the person belongs to appears in the “Automatic memberships (by rule)” preview with no remove button — membership is controlled by the rule, not by hand.
- Address book (GAL) visibility. A toggle lets you hide the employee from the Global Address List (or show them again) at any time. This is applied through Exchange Online.

Everyday changes
- Reset a password, adjust group membership, update licenses, invite a guest, re‑enable an account.
- Each action is recorded in the Activity log (Protokoll) and (depending on configuration) announced via Teams or email — see Notifications.
Watching progress
Long‑running actions appear under Live workflows on the dashboard. Completed and failed workflows show in Recent actions with a clear status.